
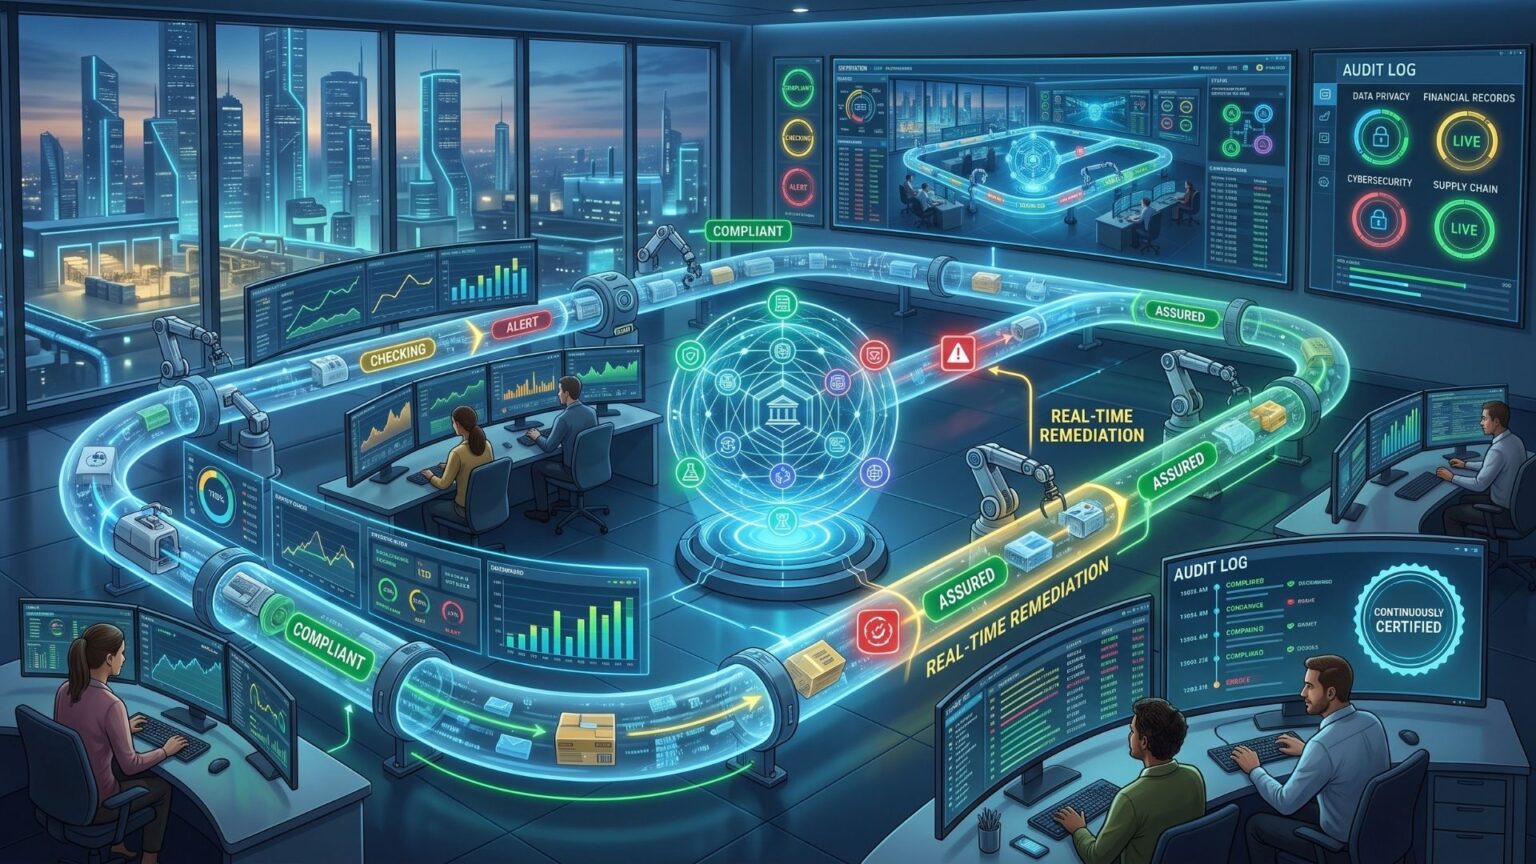
Compliance programs have traditionally relied on periodic assessments, scheduled audits, and manually collected evidence. While these activities remain important, they provide only a snapshot of an organization’s control environment at a particular point in time. Between assessments, systems change, employees join or leave, configurations are modified, and new risks can emerge. A control that passed an audit last quarter may not remain effective today.
Continuous control monitoring changes this model by making compliance an ongoing process rather than an occasional checkpoint. Instead of waiting for the next review to discover a weakness, organizations can monitor control performance as conditions change and identify exceptions closer to when they occur. This shift gives compliance, risk, and security teams a more current understanding of their control environment and helps them respond before small issues become significant findings.
Moving From Periodic Compliance Checks to Continuous Assurance
Traditional compliance monitoring often follows a predictable cycle. Teams define controls, gather evidence, perform assessments, document results, and prepare for an audit. This approach can establish accountability, but it creates an unavoidable time gap between when a control changes and when someone notices that it no longer meets requirements.
Continuous Control Monitoring addresses that gap by connecting control requirements with ongoing evidence from relevant business and technology systems. Rather than relying exclusively on manually assembled evidence, monitoring processes can evaluate information as it becomes available. A change in access permissions, an overdue review, a configuration deviation, or another control exception can therefore become visible much sooner.
The distinction is important because compliance is not inherently a quarterly or annual condition. Controls operate every day, so assurance is stronger when organizations can evaluate their effectiveness throughout that operating cycle. Continuous monitoring does not eliminate audits or formal assessments; instead, it strengthens the evidence and visibility available when those activities occur.
The approach described by Anecdotes emphasizes this progression from evidence collection and analysis toward faster identification of control gaps and ongoing reassurance after remediation.
How Continuous Control Monitoring Creates Real-Time Visibility
The practical value of continuous compliance oversight comes from connecting defined controls with the operational data that can demonstrate whether those controls are working. This may involve information from identity systems, cloud environments, ticketing platforms, endpoint tools, human resources systems, or other business applications.
When evidence is collected continuously, compliance teams can establish rules for identifying conditions that require attention. For example, an access control may require appropriate authorization for privileged accounts. If a new account receives elevated privileges outside the approved process, monitoring can identify the exception without requiring a team member to discover it during a future review.
A mature monitoring process typically performs several connected activities:
- Collect: Gather relevant evidence from authoritative business and technology systems.
- Analyze: Evaluate that evidence against defined control requirements.
- Identify: Detect exceptions, missing evidence, or changes that may affect control effectiveness.
- Notify: Route meaningful findings to the appropriate control, risk, or technical owner.
- Verify: Reassess the control after corrective action to determine whether the issue has actually been resolved.
This creates a feedback loop rather than a one-time compliance exercise. The objective is not simply to discover problems faster but to maintain a more accurate view of control performance as the environment evolves.
Turning Control Exceptions Into Actionable Risk Information
Real-time visibility is most useful when it leads to appropriate action. A monitoring system that produces hundreds of alerts without context can simply move the burden from manual evidence collection to manual alert management. Effective continuous monitoring therefore needs clear control ownership, defined thresholds, prioritization, and escalation processes.
For example, an organization may monitor whether required authentication controls are consistently enforced. If an exception occurs, the compliance team should be able to determine what changed, which control is affected, who owns the issue, and what level of risk it represents. This makes the finding actionable instead of merely informational.
The same principle applies to evidence failures. If a data source stops providing evidence, the absence itself can affect assurance. Organizations need to distinguish between a control failing and an inability to verify that the control is operating. Both conditions can require investigation.
This is where Continous Control Monitoring can improve risk management as well as compliance. By connecting control status with current evidence, organizations can make risk discussions more closely reflect operational reality. The result is a more dynamic picture than a static assessment report can provide.
Why Continuous Monitoring Strengthens Audit Readiness
Audit preparation often becomes difficult when evidence is scattered across systems, stored in different formats, or collected only shortly before an assessment. Continuous monitoring can reduce this pressure by making evidence gathering part of the normal control process.
Instead of reconstructing months of activity from emails, spreadsheets, screenshots, and system exports, teams can maintain a more consistent record of control operation. This does not mean every audit requirement can or should be automated. Human judgment remains essential for controls involving interpretation, business context, policy decisions, or management oversight.
However, automated evidence collection can reduce repetitive work and make exceptions easier to investigate. It can also help organizations identify gaps before auditors do. If a control repeatedly fails or evidence becomes unavailable, the organization has an opportunity to investigate and correct the underlying issue before it develops into a larger compliance concern.
Continuous monitoring therefore supports a more proactive audit posture. Teams are not simply preparing to demonstrate compliance at a particular moment; they are maintaining evidence and addressing control weaknesses throughout the year.
Building a Reliable Continuous Monitoring Program
Successful continuous monitoring depends on more than technology. Organizations first need to determine which controls are appropriate for ongoing monitoring and what evidence can reliably demonstrate their effectiveness. Controls should be mapped to clear requirements, assigned to accountable owners, and connected to defined response procedures.
Data quality is equally important. Monitoring is only as reliable as the evidence it evaluates. If source systems contain incomplete, outdated, or inconsistent information, automated assessments may produce misleading results. Governance over data sources, integrations, access rights, and monitoring rules is therefore an important part of the program.
Organizations should also establish practical thresholds for escalation. Not every deviation represents the same level of risk. A mature approach considers severity, business impact, affected systems, duration, and the likelihood that the issue could lead to a compliance or security failure.
Finally, remediation should include verification. Closing a ticket does not necessarily mean a control has been restored. The underlying condition should be checked again where possible. The Anecdotes CCM model similarly describes a cycle in which remediation is followed by fresh evidence collection and re-analysis so that control status can be reassessed.
End Note: Compliance as an Ongoing Operating Discipline
Continuous control monitoring represents a fundamental change in how organizations approach compliance assurance. Instead of treating compliance as a series of periodic inspections, it makes control effectiveness an ongoing operational concern. That shift provides earlier visibility into exceptions, supports faster investigation, improves evidence management, and gives leadership a more current understanding of organizational risk.
The strongest programs will not depend entirely on automation. Technology can collect evidence, identify patterns, and surface exceptions, but people remain responsible for interpreting risk, making decisions, and ensuring that corrective actions are appropriate. When continuous monitoring and human oversight work together, compliance becomes less about preparing for the next audit and more about maintaining effective controls every day.
