
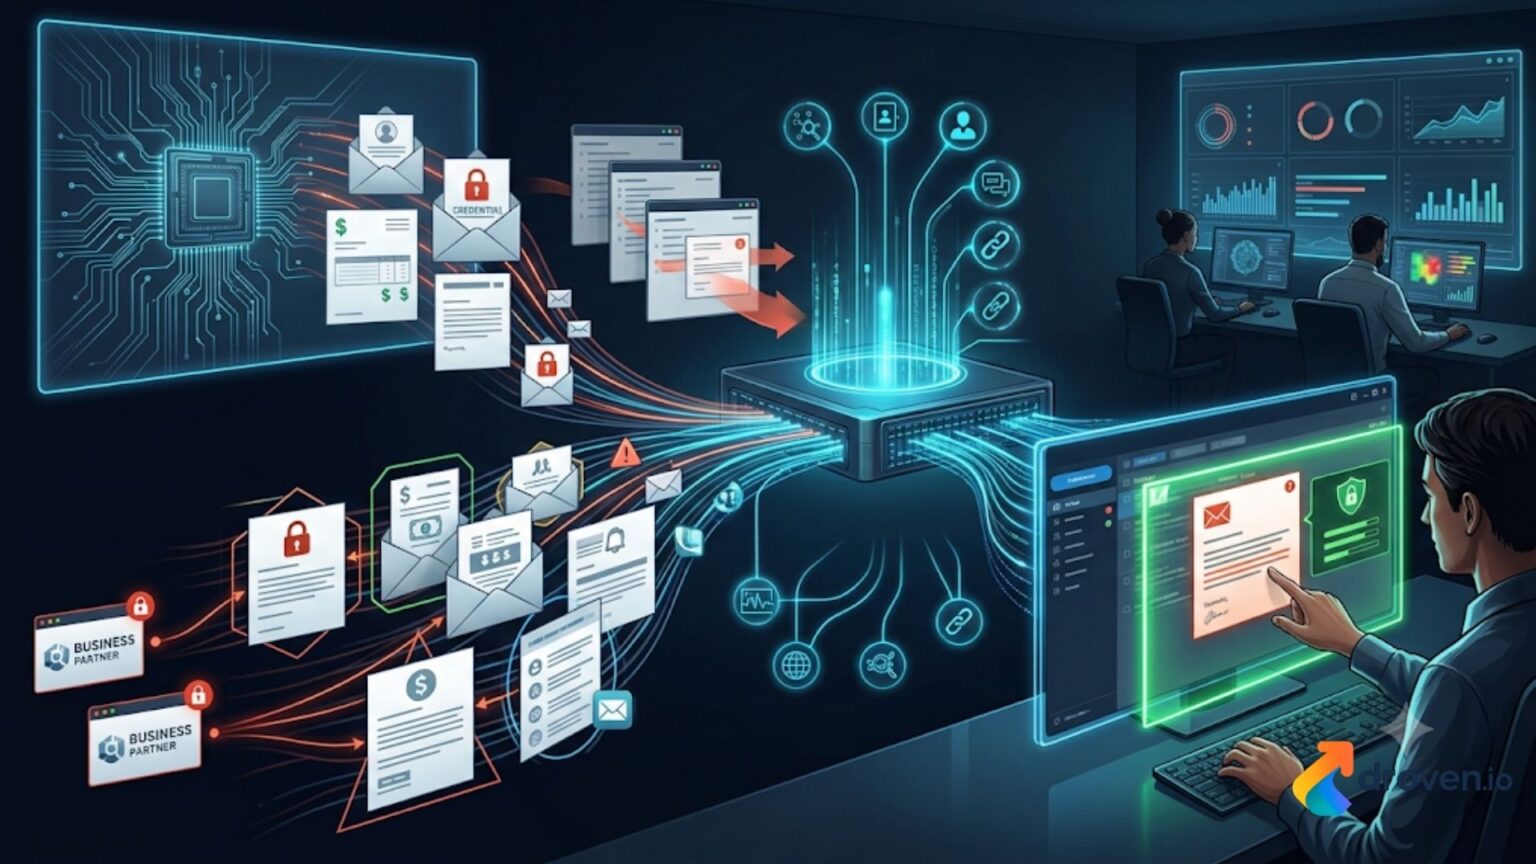
Email has always been a favorite entry point for attackers, but the nature of the threat has shifted. For years, phishing emails were relatively easy to spot: awkward phrasing, obvious spelling mistakes, and generic greetings gave them away. That is no longer a reliable defense. Generative AI tools can now produce fluent, context-aware messages that mimic the tone of a colleague, a vendor, or a company executive with unsettling accuracy. Security teams that once trained employees to recognize poor grammar as a red flag are finding that this piece of training material is quickly becoming obsolete.
The result is a phishing landscape that moves faster and looks more convincing than it did even two or three years ago. Understanding how this shift happened, and what it means for everyday email defense, is essential for anyone responsible for protecting an inbox, whether that’s a security professional or an individual user.
How AI Has Lowered the Barrier to Convincing Attacks
Traditional phishing required either skill or scale. A skilled attacker could write a convincing message but only for a handful of targets at a time. A low-skill attacker could send thousands of messages, but the quality was poor and detection rates were high. Generative AI collapses that trade-off. A single operator can now produce hundreds of uniquely worded, grammatically correct, contextually relevant emails in minutes.
Research from cybersecurity firms tracking phishing trends has repeatedly noted a rise in messages that reference real company names, recent events, or plausible internal terminology, details that used to require manual reconnaissance. Large language models can absorb publicly available information, such as a company’s press releases or an employee’s LinkedIn profile, and use it as source material to craft a message that feels personally relevant to the recipient. This is what security researchers call AI-assisted spear phishing, and it no longer requires the time investment it once did.
Why Traditional Filters Struggle to Keep Pace
Most email security systems were built around pattern recognition: known malicious links, flagged sender domains, and language patterns associated with past scams. These systems work well against repetitive, templated attacks. They are far less effective against messages that are generated fresh each time and contain no reused wording.
A few specific challenges illustrate the gap:
- Novel phrasing defeats signature-based detection. Since each AI-generated email can be worded differently, filters that rely on matching known phishing text often miss new variants entirely.
- Legitimate-looking sending infrastructure. Attackers increasingly use compromised but legitimate email accounts or newly registered domains that pass basic reputation checks.
- Believable urgency without obvious pressure tactics. Older phishing relied on panic (“Your account will be suspended!”). Newer messages use measured, professional language that mirrors how a real manager or client would write.
- Multi-step social engineering. Some campaigns now involve a benign first email to build trust before a malicious follow-up, making single-message analysis less effective.
This doesn’t mean filters are useless. Native controls and conventional security tools still block much of the mass-market spam and known malware targeting enterprise inboxes. Platforms such as Material address the harder detection and response gap created by sophisticated phishing, impersonation, and account-based threats that bypass those initial defenses. These targeted attacks are often responsible for the greatest financial damage, yet they are precisely the category traditional pattern-matching tools were not designed to identify consistently.
What the Data Shows
Independent reporting gives a sense of scale. The FBI’s Internet Crime Complaint Center has consistently ranked business email compromise among the costliest categories of cybercrime reported each year, with losses running into the billions of dollars globally. Separately, multiple security vendors that publish annual threat reports have observed measurable increases in phishing emails exhibiting characteristics consistent with AI generation, improved grammar, coherent narrative structure, and personalized detail, since large language models became widely accessible around 2023.
It’s worth being cautious about overstating this trend. Attribution is difficult; a well-written phishing email could be the product of a skilled human writer rather than an AI tool, and vendors have some incentive to frame the threat as urgent. Still, the directional evidence, more convincing language, faster campaign turnaround, and higher personalization, is consistent enough across independent sources to treat as a genuine shift rather than a passing headline.
Practical Steps for Strengthening Email Defense
Given that grammar and tone are no longer reliable tells, defense has to shift toward verification and layered controls rather than pattern-spotting alone. Some approaches worth considering:
- Verify requests involving money or credentials through a second channel, such as a phone call, rather than replying directly to the email.
- Adopt domain authentication standards like SPF, DKIM, and DMARC, which make it harder for attackers to spoof a trusted sending domain.
- Use behavioral and anomaly-based detection tools that flag unusual sending patterns or login locations rather than relying solely on content analysis.
- Update employee training material regularly to reflect current tactics, since outdated advice about spotting typos no longer covers the bulk of modern threats.
- Limit the amount of internal information published publicly, since AI tools can pull from those sources to craft more convincing messages.
None of these measures is a complete solution on its own. Layering technical controls with human verification habits tends to produce better outcomes than relying on any single defense.
What We’ve Learned
AI has not invented a new category of cybercrime — phishing and business email compromise have existed for decades. What it has done is remove many of the friction points that once limited how convincing and how frequent these attacks could be. The old advice about checking for spelling errors is no longer sufficient reference material for identifying a scam.
The more durable lesson is that email security now depends less on spotting obvious mistakes and more on verifying intent — confirming that a request is genuine before acting on it, regardless of how polished the message appears. Organizations and individuals that build this habit, alongside solid technical safeguards like domain authentication and anomaly detection, are better positioned to keep pace with a threat that continues to evolve faster than most static defenses can track.
