
For decades, digital certificates were issued to last a year, sometimes longer. That approach made sense when provisioning was manual and rotating credentials meant real operational effort. But the security landscape has changed, and the assumptions that once justified long-lived certificates no longer hold up. Today, organizations managing public key infrastructure are rethinking certificate lifespan itself as a security control, not just an administrative detail.
This shift toward short-lived certificates reflects a broader lesson learned across the security industry: the longer a credential remains valid, the longer it remains useful to an attacker. Public key infrastructure is adapting to that reality, and the changes are reshaping how certificates are issued, managed, and trusted.
Why Certificate Lifetimes Kept Shrinking
The trend toward shorter validity periods didn’t happen overnight. It followed a series of deliberate industry decisions driven by browser vendors and certificate authorities working through the CA/Browser Forum. In 2020, major browsers reduced the maximum lifespan of publicly trusted TLS certificates from 825 days to 398 days. That single change cut the exposure window for a compromised or misconfigured certificate by more than half.
The reasoning was straightforward. A certificate that’s valid for two years gives an attacker who steals its private key two years of potential misuse before the credential naturally expires. Shortening that window doesn’t eliminate the risk of key compromise, but it limits how long the damage can persist if revocation fails or goes unnoticed, which happens more often than most organizations would like to admit.
Revocation checking has long been a weak point in public key infrastructure. Certificate Revocation Lists and the Online Certificate Status Protocol both depend on clients actually checking status in real time, and both have well-documented reliability and performance issues. When revocation can’t be trusted to work consistently, reducing the validity period becomes a more dependable backstop.
What Short-Lived Certificates Actually Change
Short-lived certificates typically refers to credentials valid for days, hours, or in some automated environments, even minutes. This is a significant departure from the annual renewal cycle many organizations are used to. The core idea is simple: if a certificate expires quickly enough, a stolen or misused key has a naturally limited shelf life, regardless of whether anyone notices the compromise.
This matters because certificate compromise doesn’t always announce itself. Private keys can be exposed through misconfigured servers, compromised build pipelines, or insider mishandling, and the gap between compromise and detection can stretch for weeks or months. According to IBM’s Cost of a Data Breach research, the average time to identify and contain a breach has consistently been measured in months rather than days. A certificate that automatically expires within that window closes off an avenue of persistent access, even if the breach itself hasn’t been discovered yet.
Short-lived certificates also reduce reliance on revocation infrastructure altogether. Instead of asking “did the revocation check succeed,” the question becomes “has this certificate already expired.” That’s a much simpler and more reliable trust model, particularly in distributed systems where revocation checks can be slow, blocked by firewalls, or skipped entirely for performance reasons.
The Automation Requirement Behind the Shift
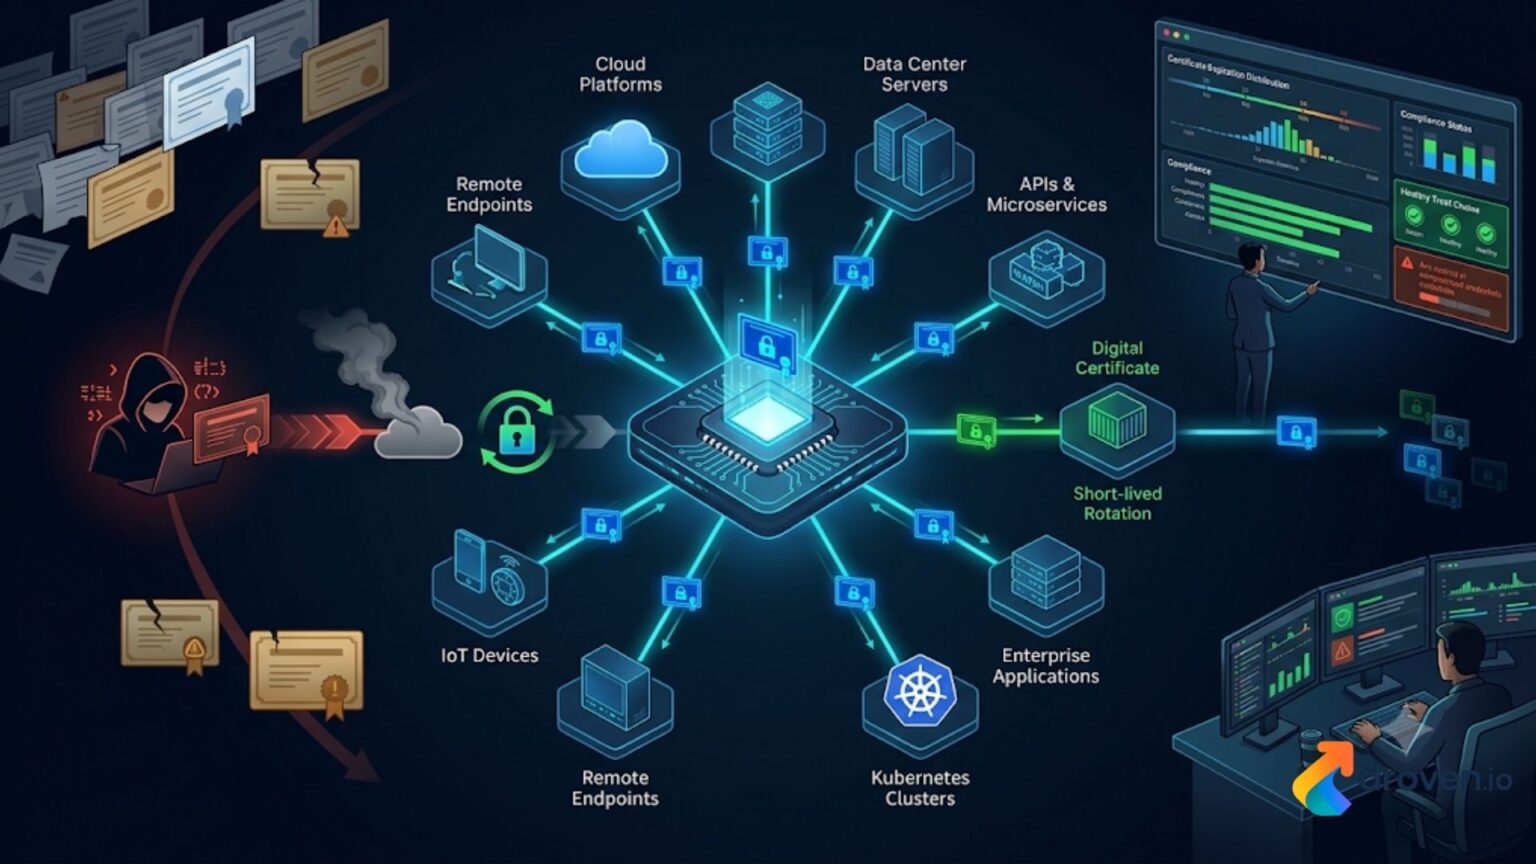
None of this works without automation. Manually renewing certificates every 90 days across thousands of endpoints isn’t realistic, let alone renewing them daily. This is why the rise of short-lived certificates has moved in lockstep with the adoption of automated certificate management, most notably through protocols like ACME (Automated Certificate Management Environment), which underpins services like Let’s Encrypt.
Systems built around public key infrastructure with short certificate validity periods generally require a few structural changes to function reliably:
- Automated issuance and renewal, so certificates are replaced before expiry without manual intervention
- Centralized visibility, giving administrators a live inventory of every certificate and its expiration status
- Standardized protocols, such as ACME, that allow issuance and renewal to be scripted and repeated across environments
- Monitoring and alerting, to catch renewal failures before they cause outages
- Integration with orchestration tools, particularly in containerized and cloud-native environments where services are created and destroyed frequently
Organizations that adopt short-lived certificates without building this automation layer tend to run into a different problem: outages caused by expired certificates that nobody renewed in time. This is a well-known risk. Multiple high-profile service disruptions over the past several years have traced back to a single expired certificate that fell through the cracks. Shortening lifespans without solid automation simply trades one risk for another.
Where This Fits Within Broader PKI Strategy
Short-lived certificates aren’t a replacement for sound public key infrastructure practices; they’re an extension of them. Strong key management, proper certificate authority hierarchies, and clear policies for issuance still matter as much as they always did. What changes is the operational tempo. Instead of certificates being a “set it and forget it” annual task, they become a continuously managed, machine-driven process.
This is particularly relevant in service mesh and microservices architectures, where internal services authenticate to each other constantly and at scale. In these environments, certificates with lifespans measured in hours are becoming a practical norm rather than an edge case, since automated systems can handle the renewal load that would overwhelm a manual process.
It’s also worth noting that shorter lifespans don’t inherently improve cryptographic strength. The algorithms and key lengths underlying a certificate matter just as much as before. Short-lived certificates address exposure time, not the underlying strength of the cryptography itself. Both dimensions need attention for a public key infrastructure deployment to be considered genuinely resilient.
What We’ve Learned
The move toward short-lived certificates reflects a maturing understanding of risk in public key infrastructure: static, long-lived trust is harder to defend than trust that refreshes itself frequently and automatically. Shorter lifespans reduce the window of opportunity for compromised keys, lessen dependence on revocation systems that don’t always work as intended, and push organizations toward automation that pays off in reliability as well as security.
The tradeoff is operational complexity. Without solid automation, shorter certificate lifespans introduce a real risk of outages from missed renewals. But for organizations that build the right infrastructure to support it, shorter-lived certificates represent a meaningful reduction in attack surface, one grounded not in theory but in the practical reality of how credentials get compromised and how long that compromise typically goes unnoticed.
